
Approach
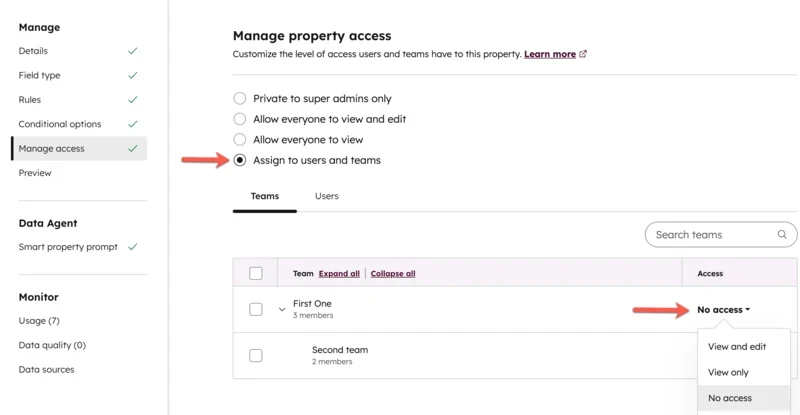
For each account and permission, we define who is responsible, why access is needed and what that person is allowed to do.
How we work
We audit users, roles, tools, and sensitive data.
We organize permissions by role and remove unnecessary access.
We document owners, backups, and critical changes.
How this connects to your business
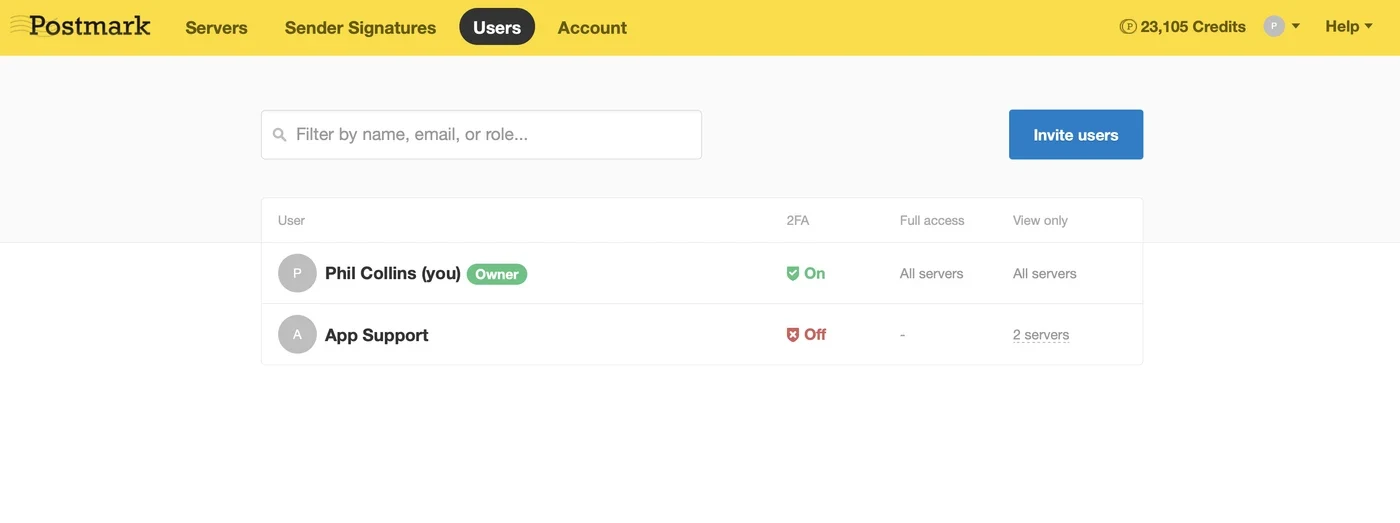
We request the permissions needed for the work and separate them by role. We avoid shared passwords and record who controls critical accounts so the team knows whom to contact if something changes or goes wrong.
What to define
We choose connections based on the work they need to do. An integration can prevent entering a contact twice, reduce recording errors or send the data someone needs to another tool.
- Which system holds the authoritative record of contacts, opportunities, payments or tickets.
- Which fields we send, in which format and what needs to happen to send them.
- How we'll test the connection before putting it into use.
Expected outcome
Each tool receives the data it needs. If a connection fails, the team gets an alert so it can investigate.
Tools for the project
We choose them to suit the task, the access you have and the data you need to keep.
- Clerk
- GitHub
- Cloudflare
- Google Cloud
- Microsoft Azure